Explanation:
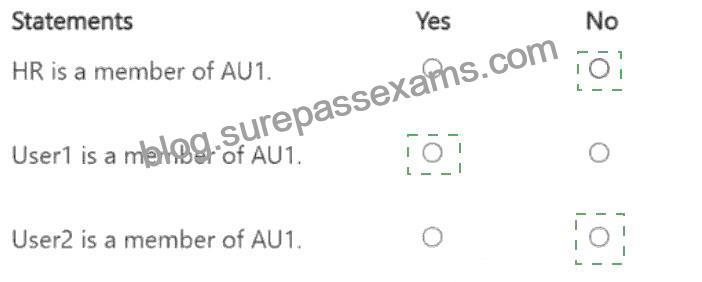
HR is a member of AU1: No
User1 is a member of AU1: Yes
User2 is a member of AU1: No
Let’s break this down step by step based on Microsoft Entra ID dynamic membership rules, administrative units, and group membership, as outlined in Microsoft Identity and Access Administrator documentation.
Understanding Administrative Units and Dynamic Membership in Microsoft Entra ID:
Administrative Units (AUs):Administrative Units in Microsoft Entra ID are used to delegate administrative tasks to a subset of users, groups, or devices. They allow you to scope administrative roles (e.g., User Administrator) to specific users or groups within the AU.
Membership Types for AUs:
Assigned Membership:Members (users, groups, or devices) are manually added to the AU by an administrator.
Dynamic Membership:Members are automatically added or removed based on a dynamic membership rule, similar to dynamic groups. Dynamic membership for AUs can be applied to users or devices (but not groups directly).
The question states that AU1 is initially configured for assigned membership but is then updated to useDynamic Usermembership with the rule (user.department -eq “HR”).
Dynamic Membership Rule:The rule (user.department -eq “HR”) means that AU1 will automatically include all users whose department attribute in Microsoft Entra ID is set to “HR”. This rule applies to users, not groups or devices, because the membership type is “Dynamic User.” Impact of Changing AU1 to Dynamic Membership:
When AU1’s membership type is changed from assigned to dynamic, the existing assigned memberships (e.
g., User2, HR group, IT group) are no longer relevant. Thedynamic rule takes over, and AU1’s membership is determined solely by the rule (user.department -eq “HR”).
Dynamic User Membership:Only users whose attributes match the rule will be members of AU1. Groups (like HR and IT) are not evaluated by this rule because the membership type is “Dynamic User,” not “Dynamic Group.” Let’s evaluate the users based on the rule:
User1:Department = “HR”. The rule (user.department -eq “HR”) matches, so User1 will be dynamically added to AU1.
User2:Department = “IT”. The rule does not match, so User2 will not be a member of AU1, even though they were previously assigned to AU1 and are a member of the IT group.
Groups (HR and IT):The dynamic membership rule for AU1 applies to users, not groups. Therefore, groups like HR and IT are not directly evaluated by the rule. However, we need toconsider whether group membership in AU1 affects the statements.
Statement 1: HR is a member of AU1:
Analysis:
The HR group is listed in the second table with AU1 as its administrative unit, indicating that it was initially assigned to AU1 when AU1 used assigned membership.
However, AU1’s membership type has been updated to “Dynamic User” with the rule (user.department -eq
“HR”). Dynamic User membership applies to users, not groups.
In Microsoft Entra ID, administrative units with dynamic user membership do not include groups as members unless the AU’s membership type is explicitly set to “Dynamic Group” (which is not the case here).
When AU1 was changed to dynamic membership, the HR group would no longer be considered a member of AU1 because the dynamic rule only evaluates users. Groups are not dynamically added to AUs based on user attributes.
Conclusion:The HR group is not a member of AU1 after the change to dynamic membership. Therefore, this statement isNo.
Statement 2: User1 is a member of AU1:
Analysis:
User1 has the department attribute set to “HR” (from the first table).
The dynamic membership rule for AU1 is (user.department -eq “HR”), which matches User1’s department.
Therefore, User1 will be automatically added to AU1 as a member based on the dynamic rule.
Additionally, User1 is a member of the HR group, which was initially assigned to AU1. However, since AU1 now uses dynamic membership, the HR group’s assignment to AU1 is irrelevant. User1’s membership in AU1 is determined solely by the dynamic rule, not their group membership.
Conclusion:User1 is a member of AU1 because their department matches the dynamic rule. Therefore, this statement isYes.
Statement 3: User2 is a member of AU1:
Analysis:
User2 has the department attribute set to “IT” (from the first table).
The dynamic membership rule for AU1 is (user.department -eq “HR”), which does not match User2’s department.
User2 was initially assigned to AU1 (as shown in the first table) and is a member of the IT group, which was also assigned to AU1. However, when AU1’s membership type was changed to “Dynamic User,” the assigned memberships (including User2 and the IT group) are no longer relevant.
The dynamic rule only includes users with the department “HR,” so User2 is not added to AU1.
Conclusion:User2 is not a member of AU1 because their department does not match the dynamic rule.
Therefore, this statement isNo.
Additional Considerations:
If AU1’s membership type were “Dynamic Group” instead of “Dynamic User,” we would evaluate whether the HR and IT groups match a group-based rule. However, the question specifies “Dynamic User,” so the rule applies to user attributes only.
The initial assigned memberships (e.g., User2, HR group, IT group) are overridden by the dynamic membership rule. Microsoft Entra ID does not retain assigned memberships when an AU or group is converted to dynamic membership.
The HR and IT groups being assigned to AU1 initially does not affect the dynamic membership of users, but it might be relevant for administrative scoping (e.g., if an admin role is scoped to AU1). However, the statements are about membership, not administrative roles.
Conclusion:Based on the dynamic membership rule (user.department -eq “HR”) for AU1:
HR group:Not a member of AU1 because dynamic user membership does not apply to groups.
User1:A member of AU1 because their department is “HR,” matching the rule.
User2:Not a member of AU1 because their department is “IT,” which does not match the rule.Therefore, the answers are:
HR is a member of AU1:No
User1 is a member of AU1:Yes
User2 is a member of AU1:No
References:
Microsoft Entra ID documentation: “Dynamic membership rules for groups and administrative units” (Microsoft Learn:https://learn.microsoft.com/en-us/entra/identity/users/groups-dynamic-membership) Microsoft Entra ID documentation: “Manage administrative units” (Microsoft Learn:https://learn.microsoft.
com/en-us/entra/identity/role-based-access-control/administrative-units) Microsoft Identity and Access Administrator (SC-300) exam study guide, which covers dynamic membership rules and administrative units in Microsoft Entra ID.


